We’re committed to protect you!
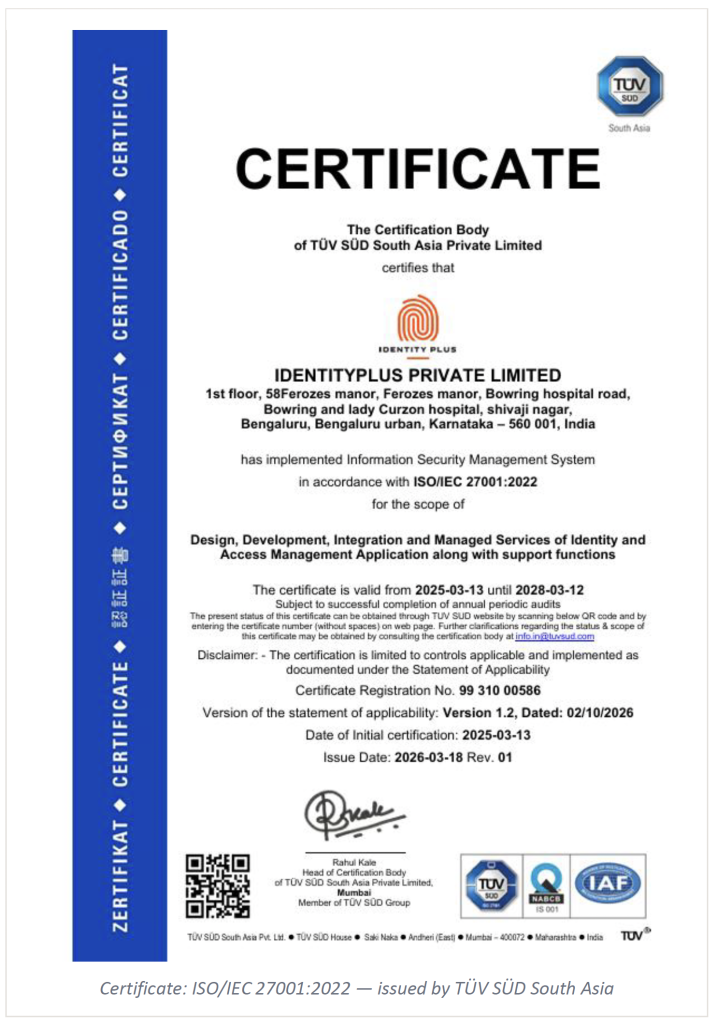
Information Security Management
The global benchmark for information security management systems
Confirms we run a systematic, risk-based program to protect the confidentiality,
integrity, and availability of information across our platforms. This gives customers
assurance that security risks are identified, managed, and mitigated on an ongoing
basis, not addressed only after an incident.
integrity, and availability of information across our platforms. This gives customers
assurance that security risks are identified, managed, and mitigated on an ongoing
basis, not addressed only after an incident.
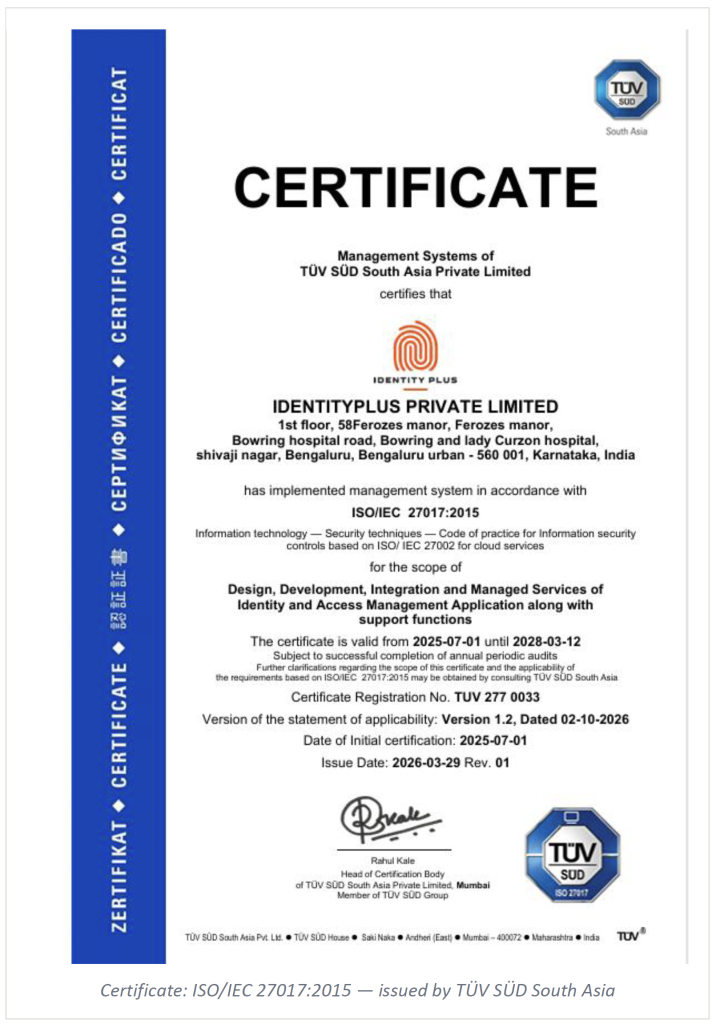
Cloud Security Controls
Sector-specific controls for cloud service security
Extends our ISO 27001 foundation with controls built specifically for cloud
environments: clear division of security responsibilities between us and our cloud
partners, secure segregation of customer data in shared infrastructure, and
defenses against misconfiguration and insecure interfaces.
environments: clear division of security responsibilities between us and our cloud
partners, secure segregation of customer data in shared infrastructure, and
defenses against misconfiguration and insecure interfaces.
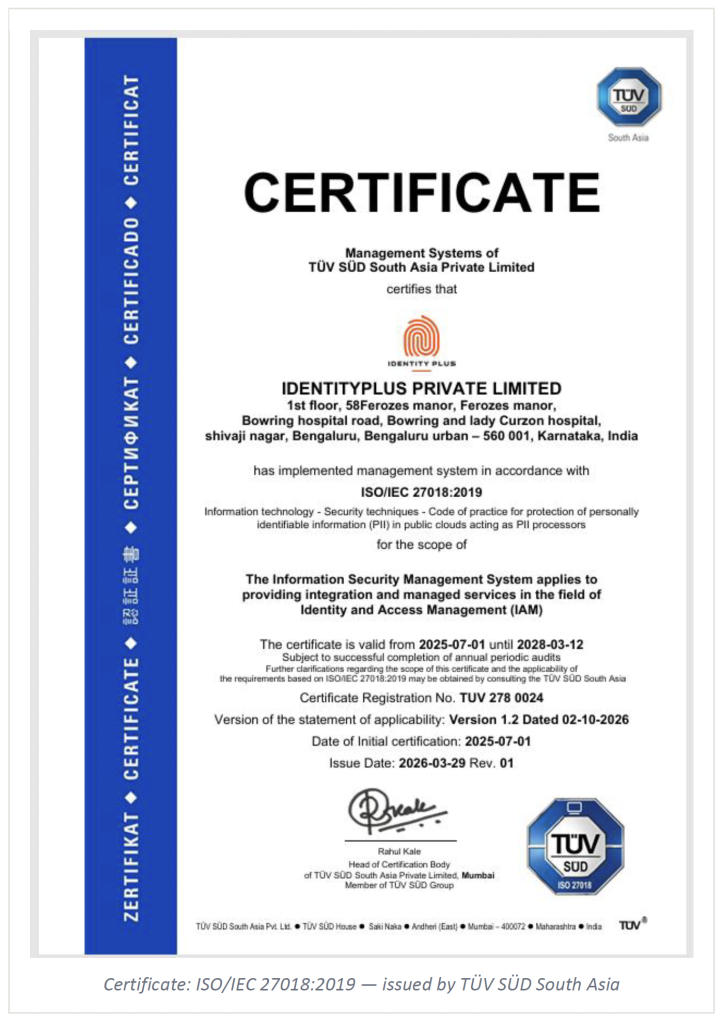
Protection of Personal Data in the Cloud
The first international standard for PII protection in the public cloud
Governs how we handle personally identifiable information as a cloud processor:
data is used only for agreed purposes, consent is obtained before any additional
use, customers are notified promptly of any breach, and secure deletion or return
of data is guaranteed once it’s no longer needed.
data is used only for agreed purposes, consent is obtained before any additional
use, customers are notified promptly of any breach, and secure deletion or return
of data is guaranteed once it’s no longer needed.
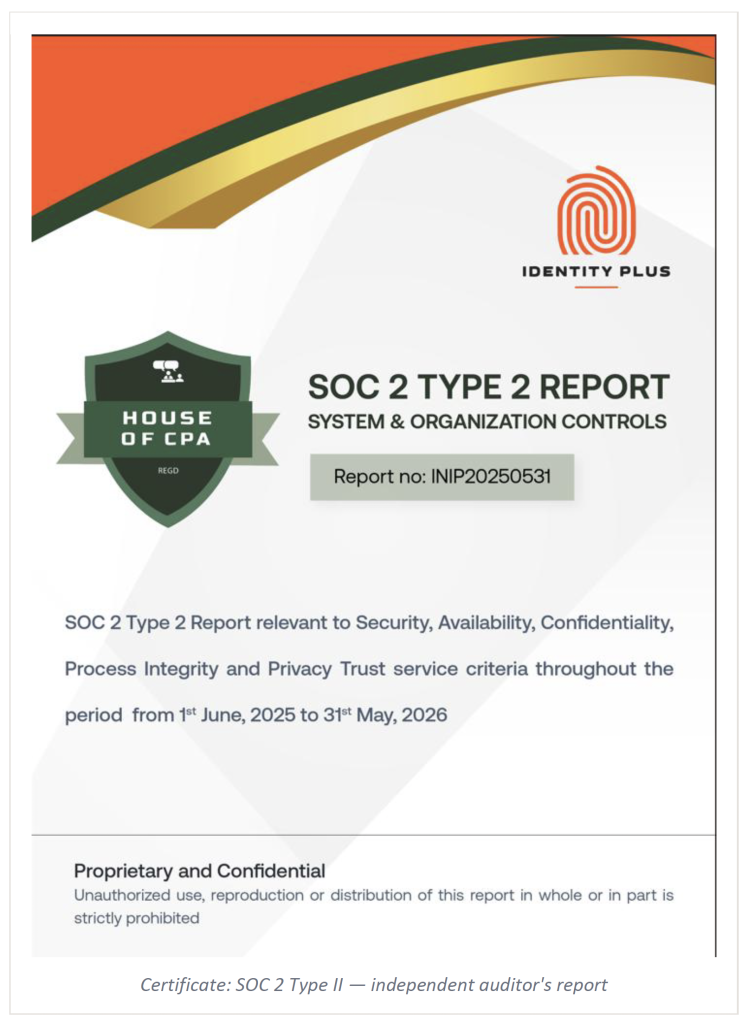
Trust Services Criteria
Independently audited controls, proven effective over time
Independently audited controls, proven effective over time
Verified by an independent third-party auditor against the Security, Availability,
Processing Integrity, Confidentiality, and Privacy criteria — and, unlike a point-in
time review, Type II confirms these controls held up under real operating
conditions over a sustained audit period.
Processing Integrity, Confidentiality, and Privacy criteria — and, unlike a point-in
time review, Type II confirms these controls held up under real operating
conditions over a sustained audit period.
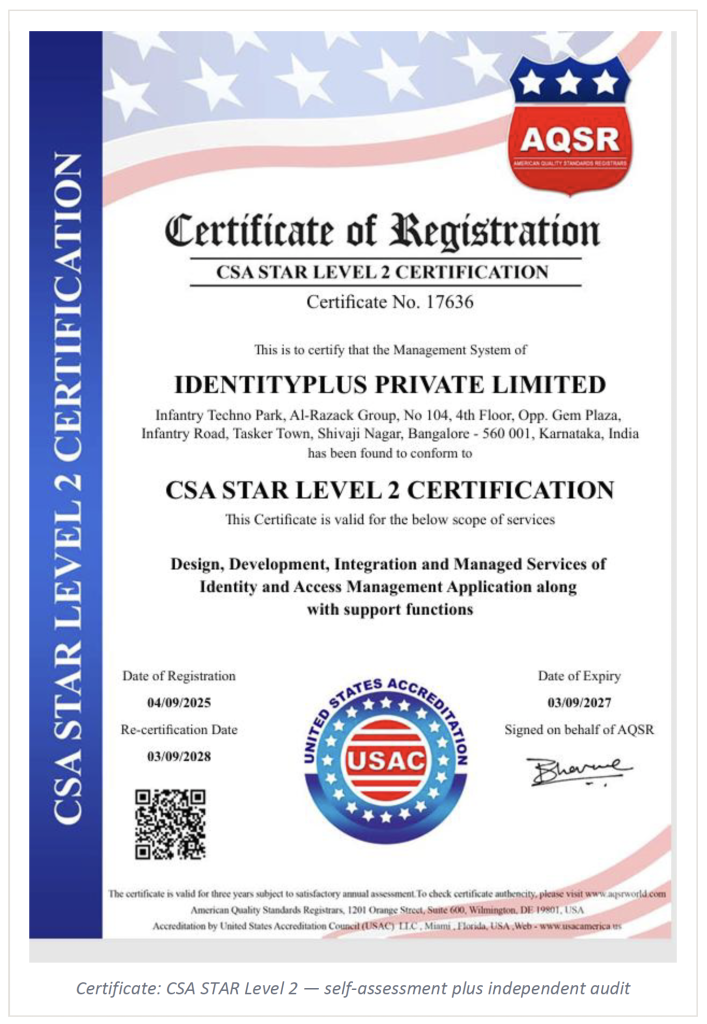
Cloud Security Assurance
The cloud industry’s most comprehensive assurance framework
Layers a rigorous, independent assessment against the Cloud Security Alliance’s
Cloud Controls Matrix on top of our ISO 27001 and SOC 2 Type II certifications —
demonstrating mature risk management, governance, and transparency
specifically for cloud-delivered services.